CriticalVulnerability
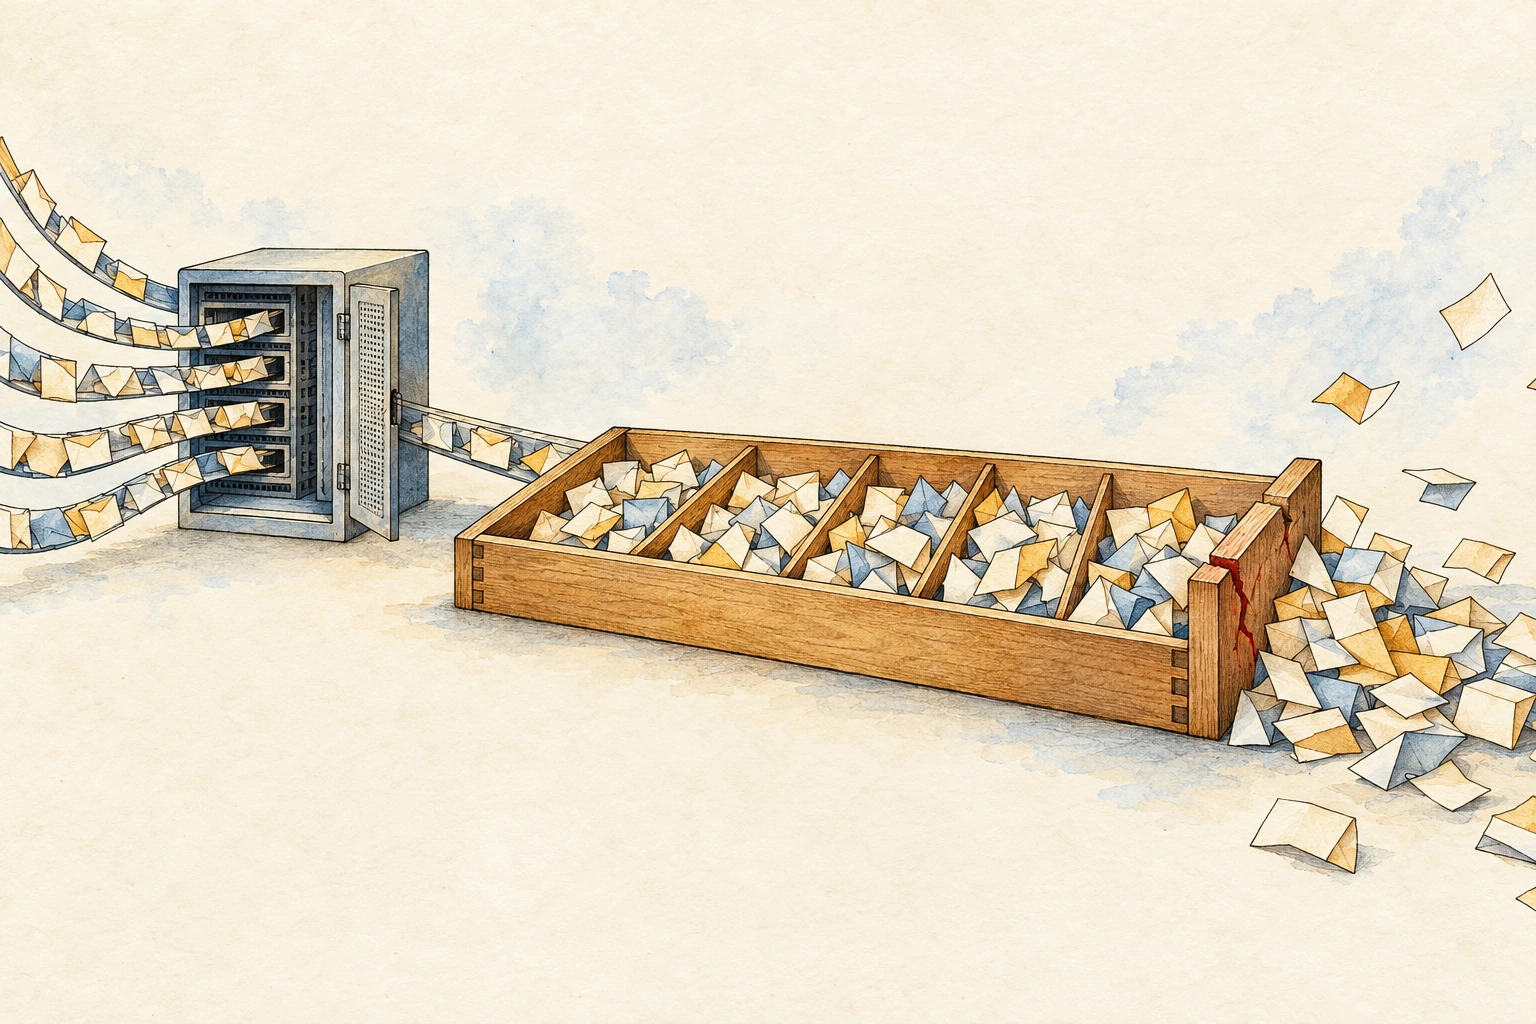
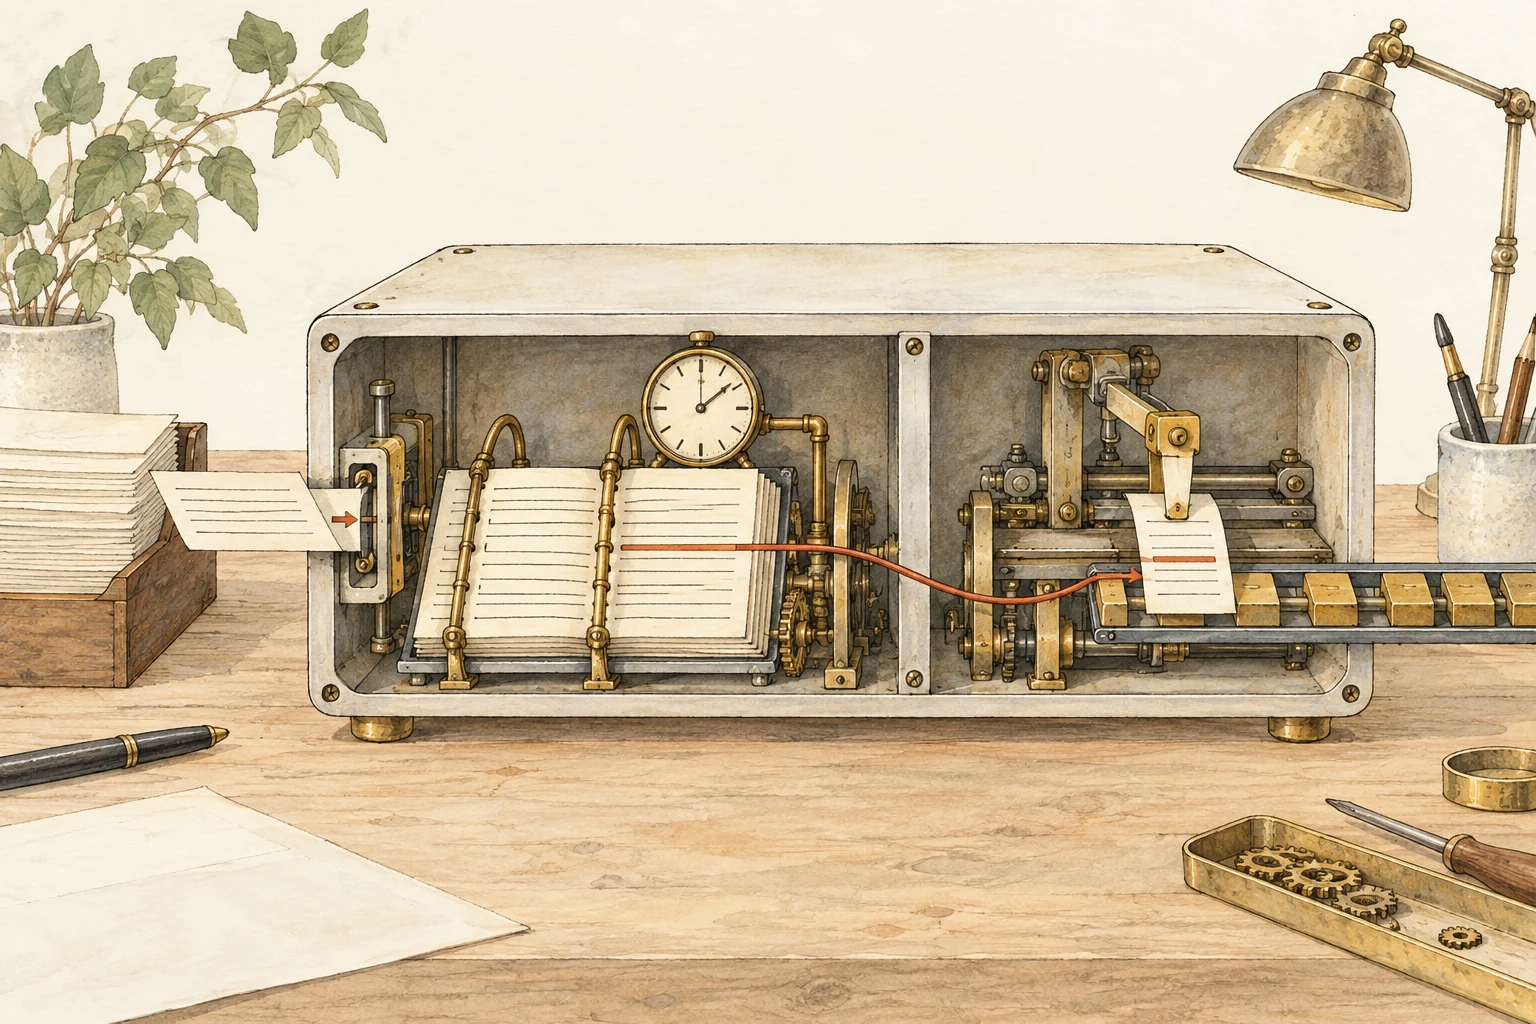
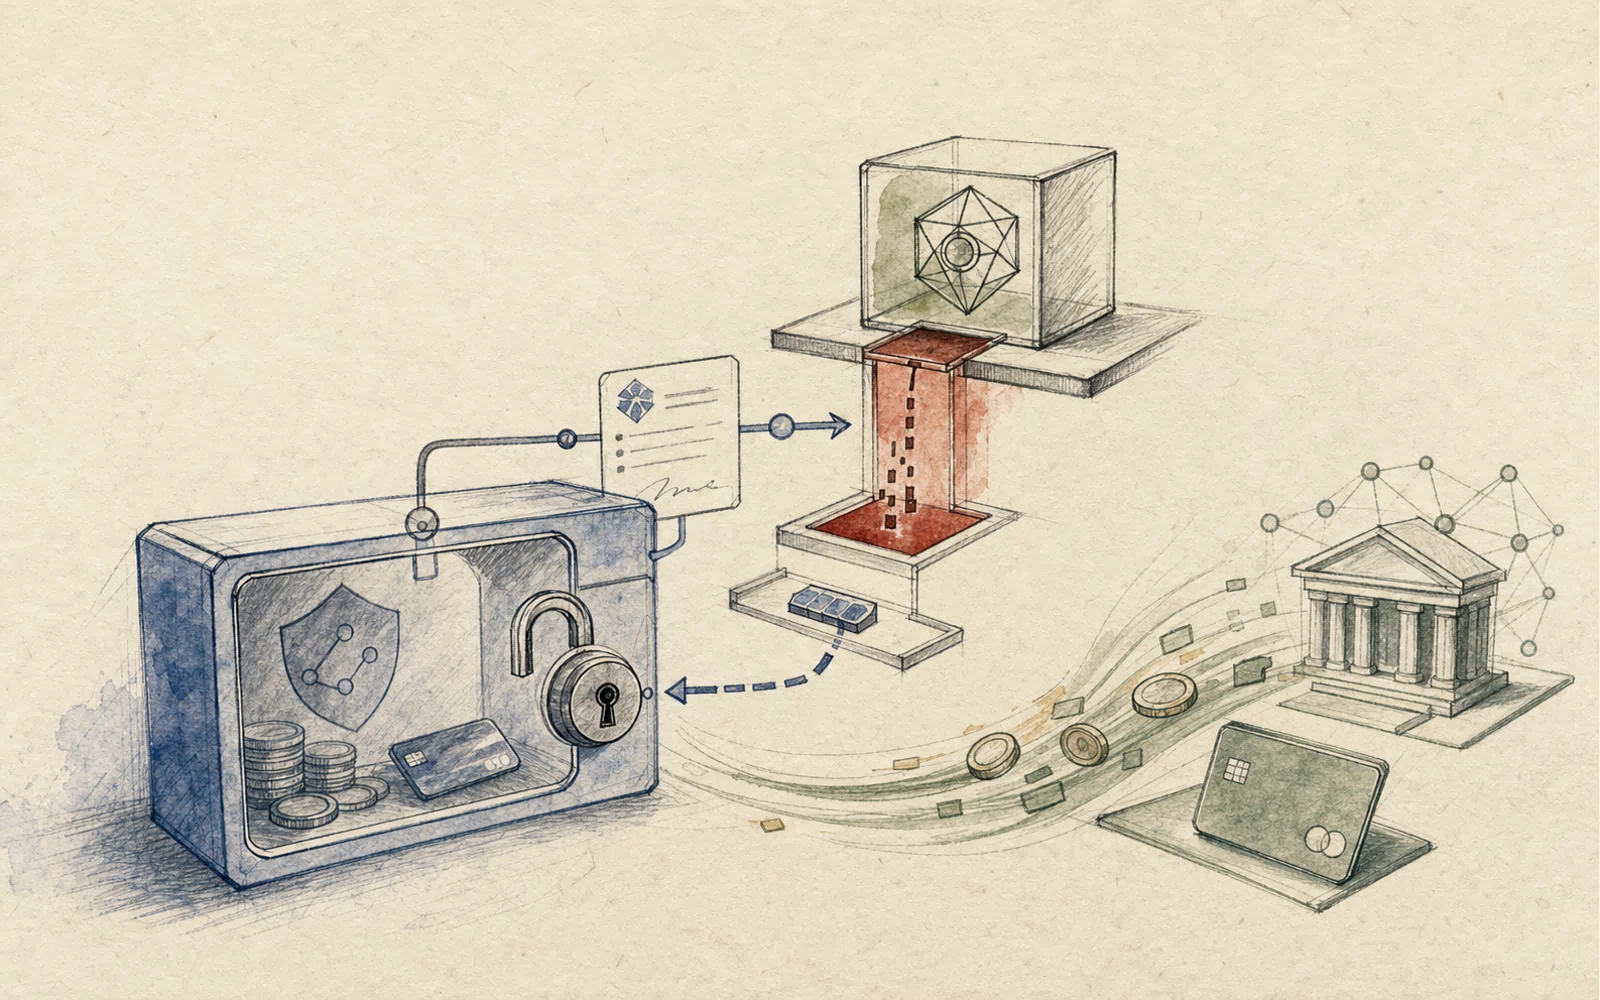
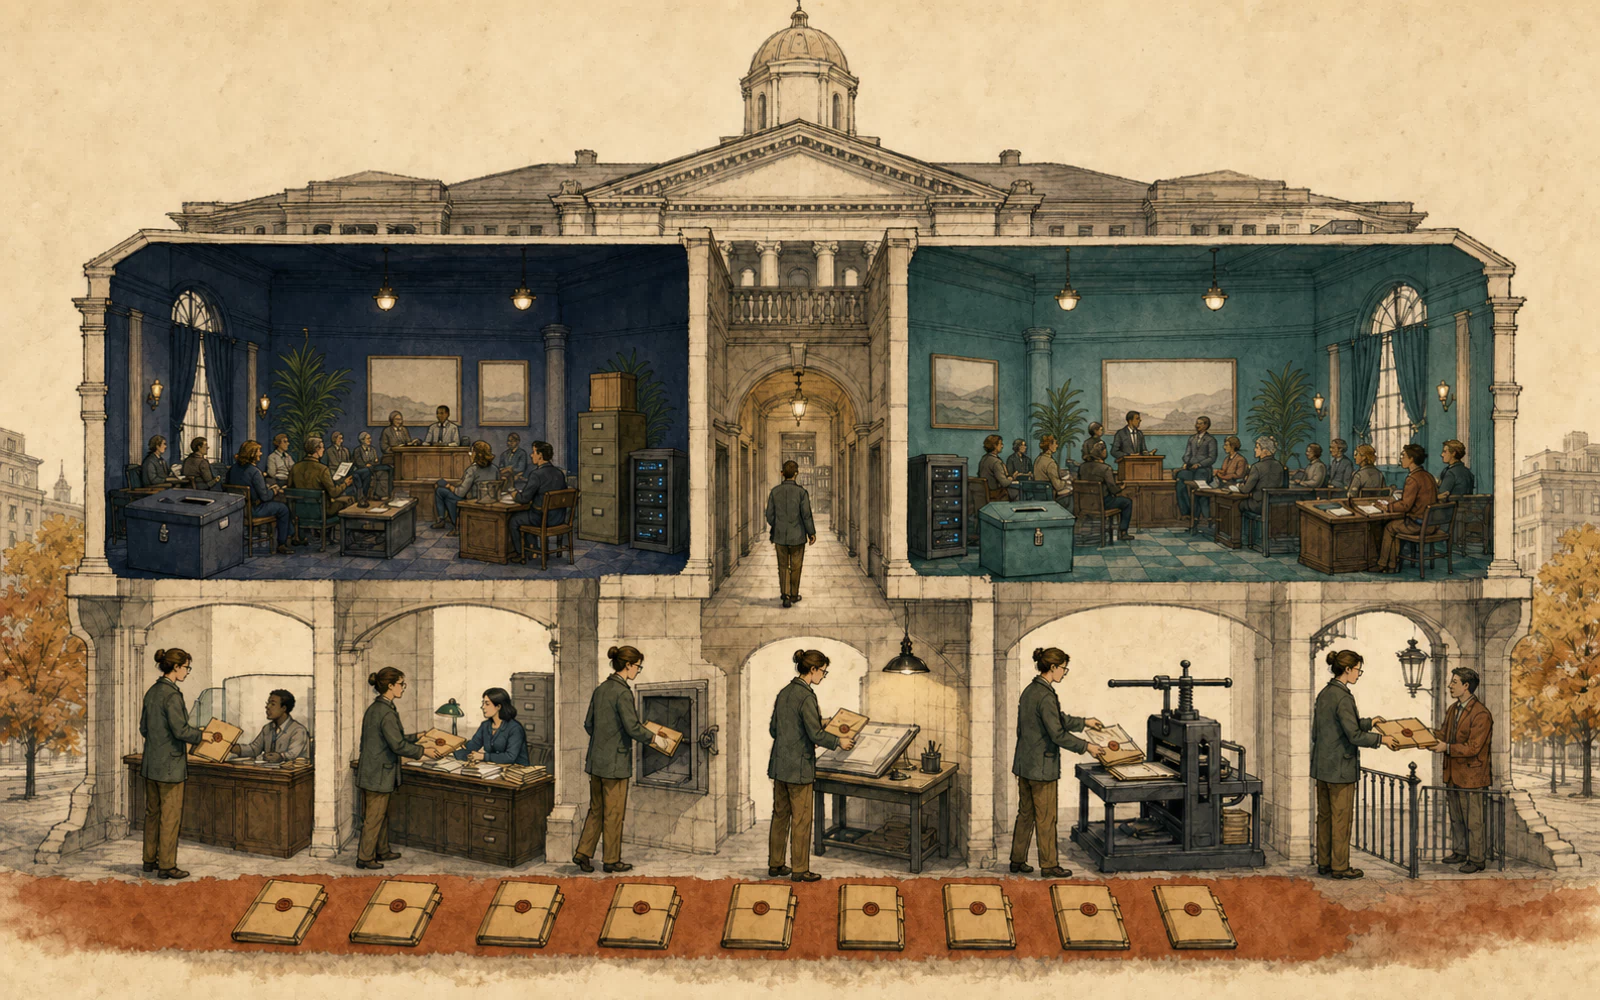
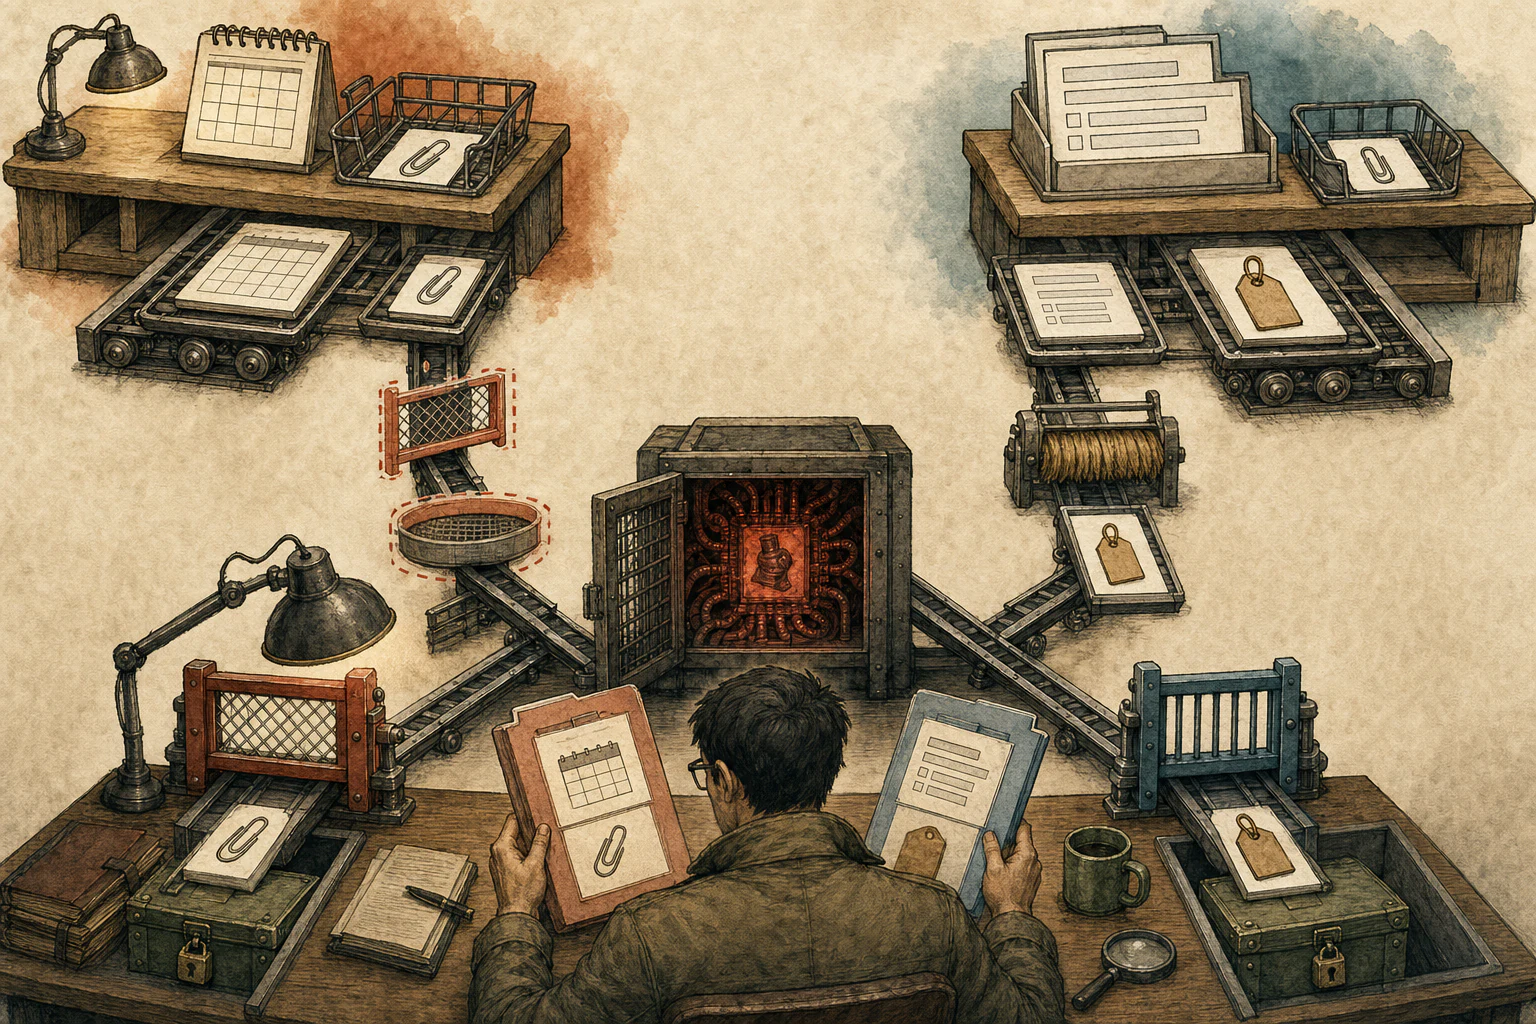
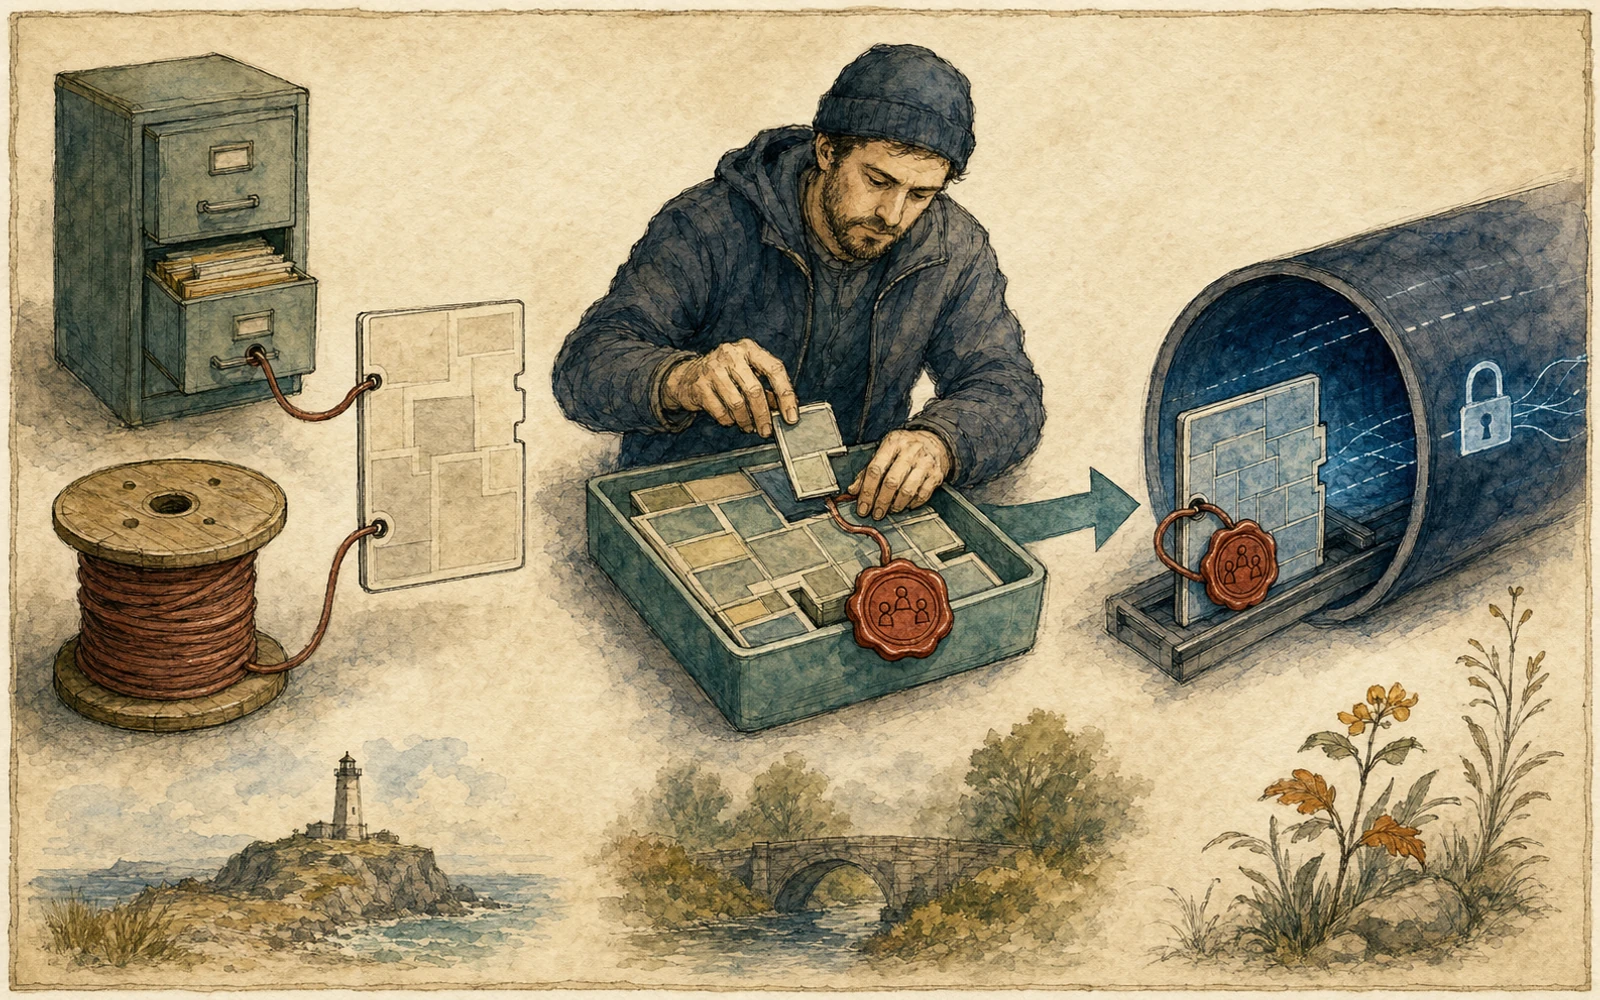
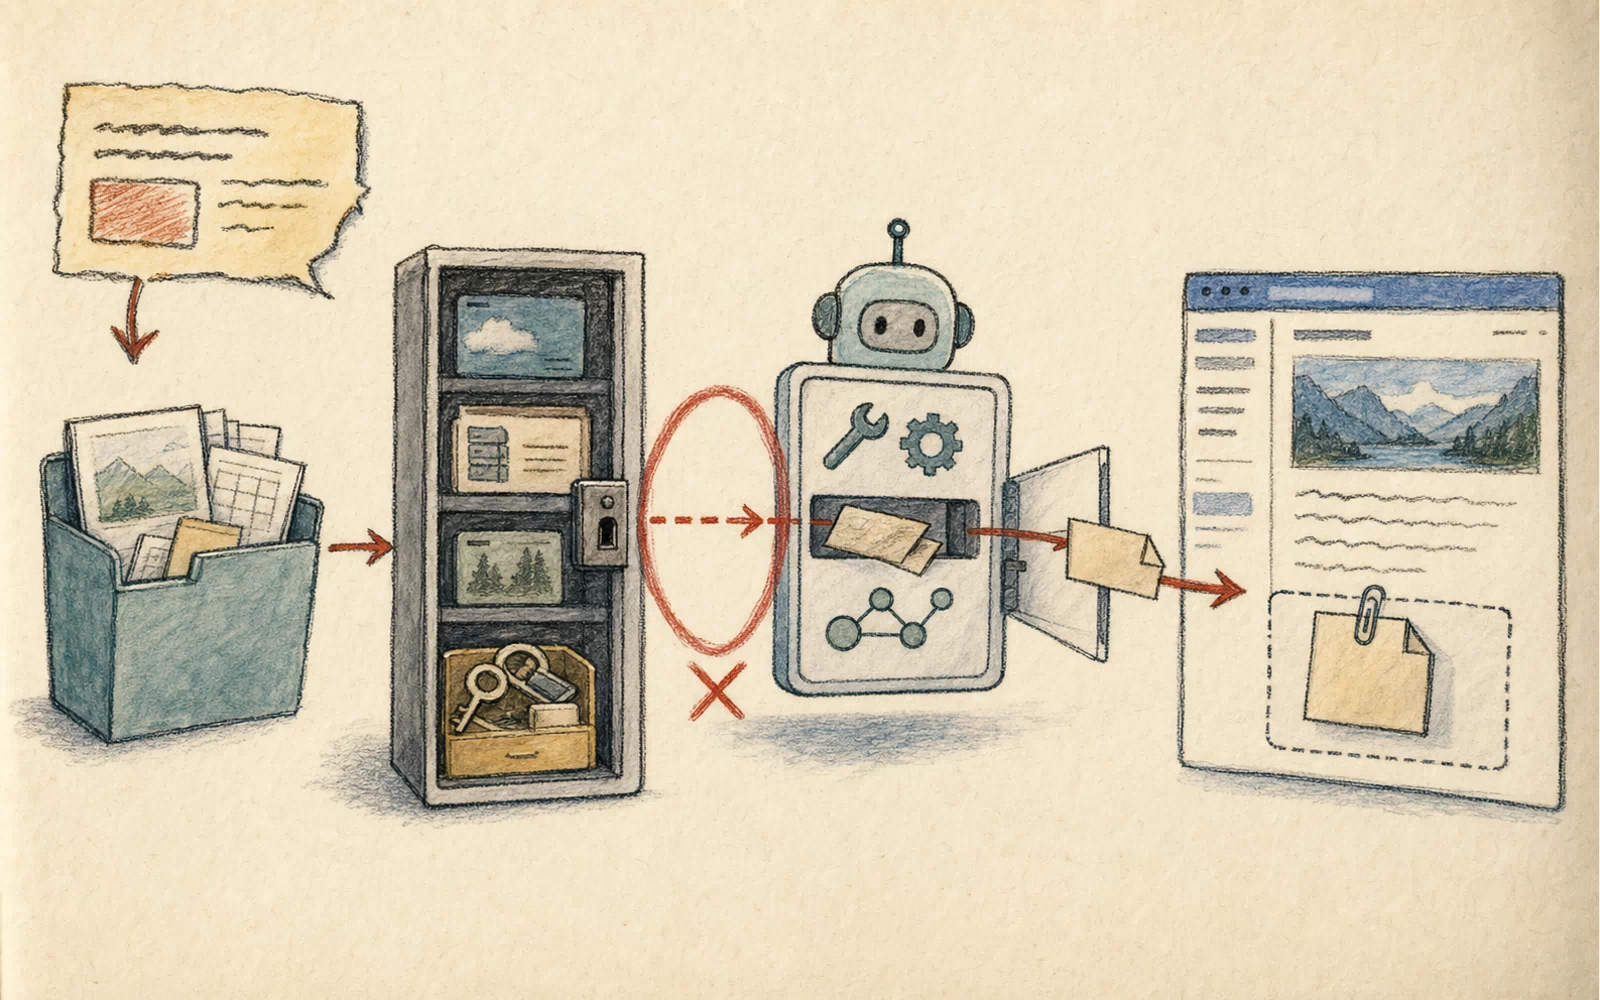
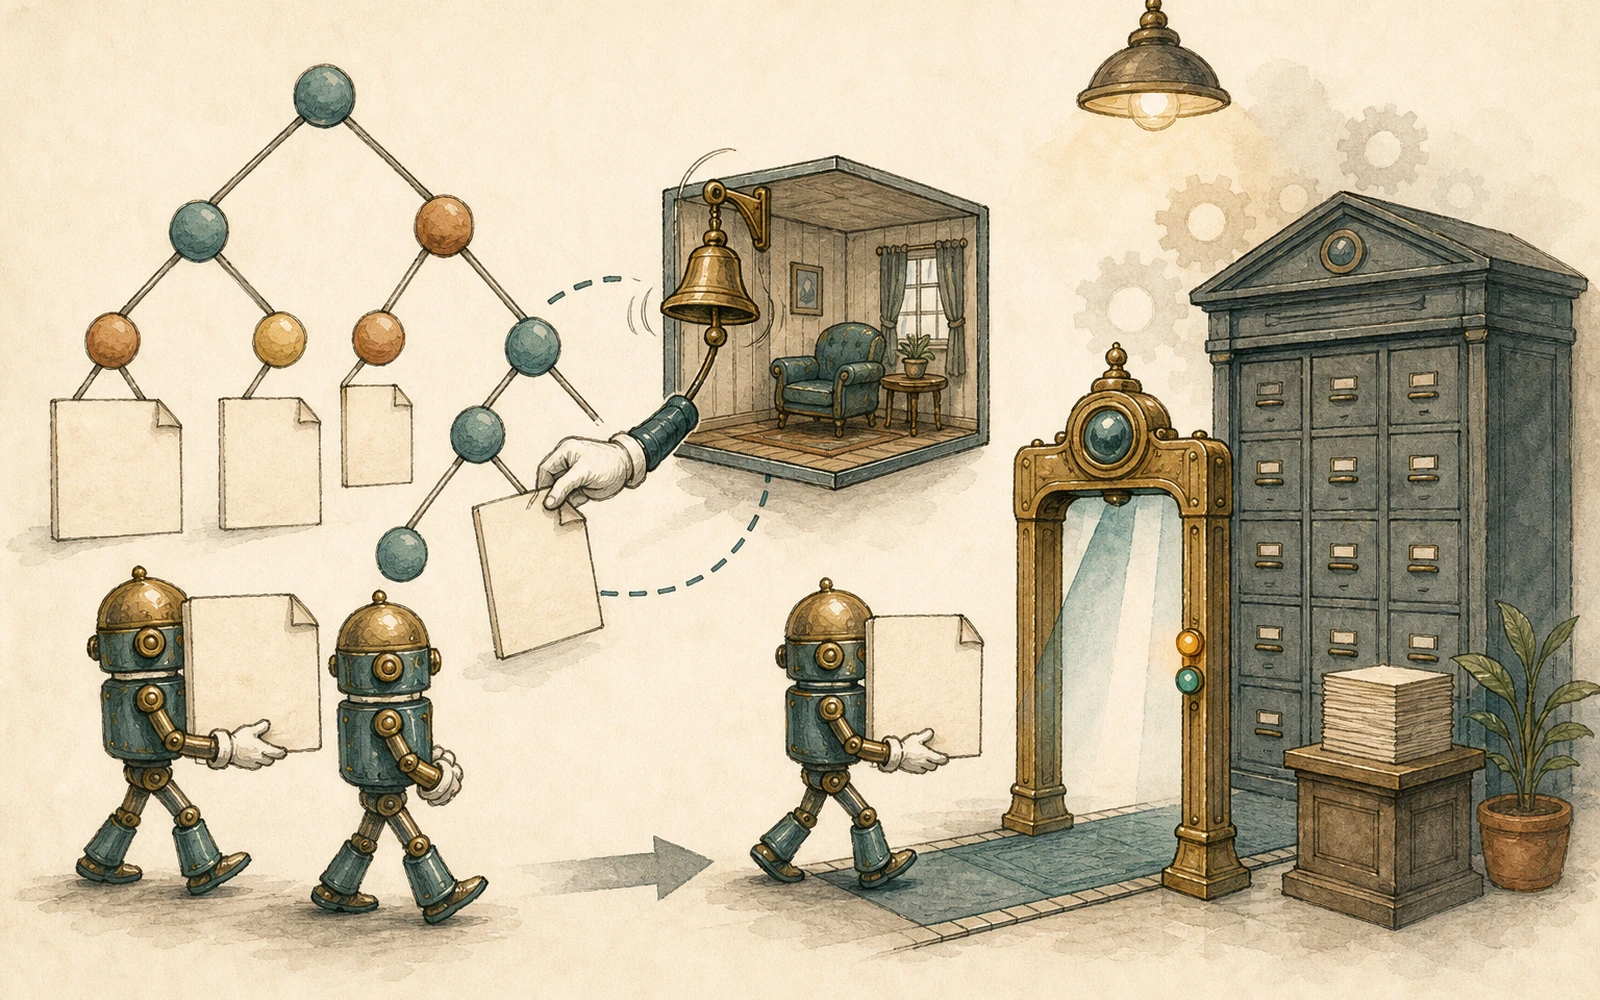
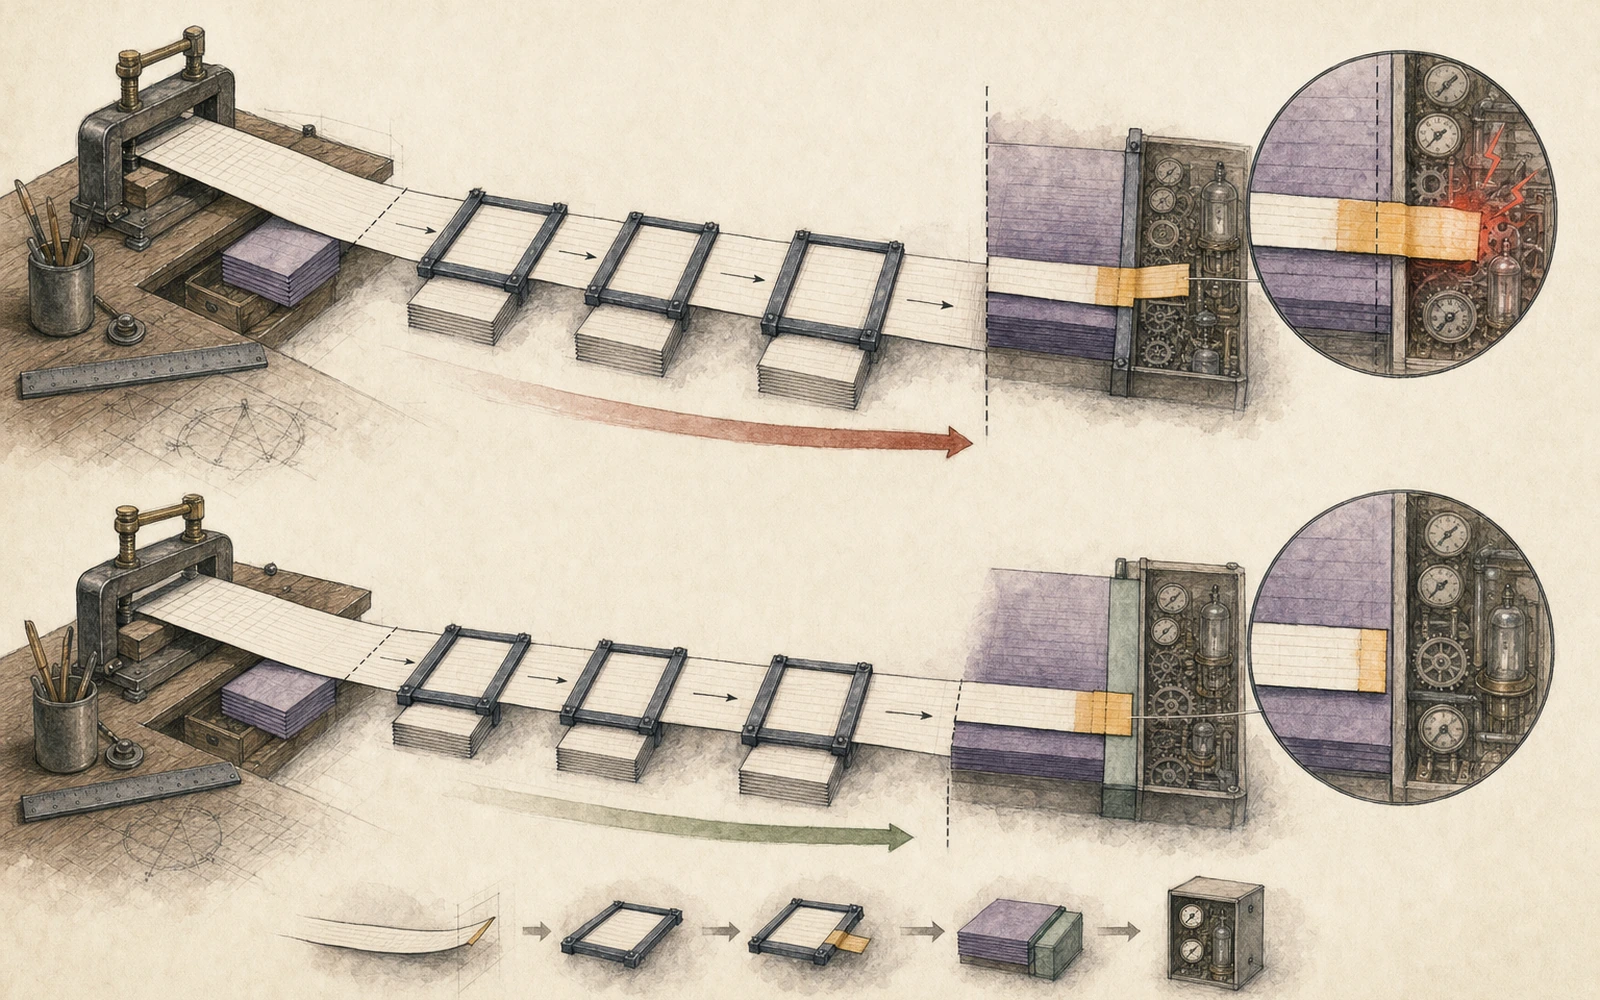
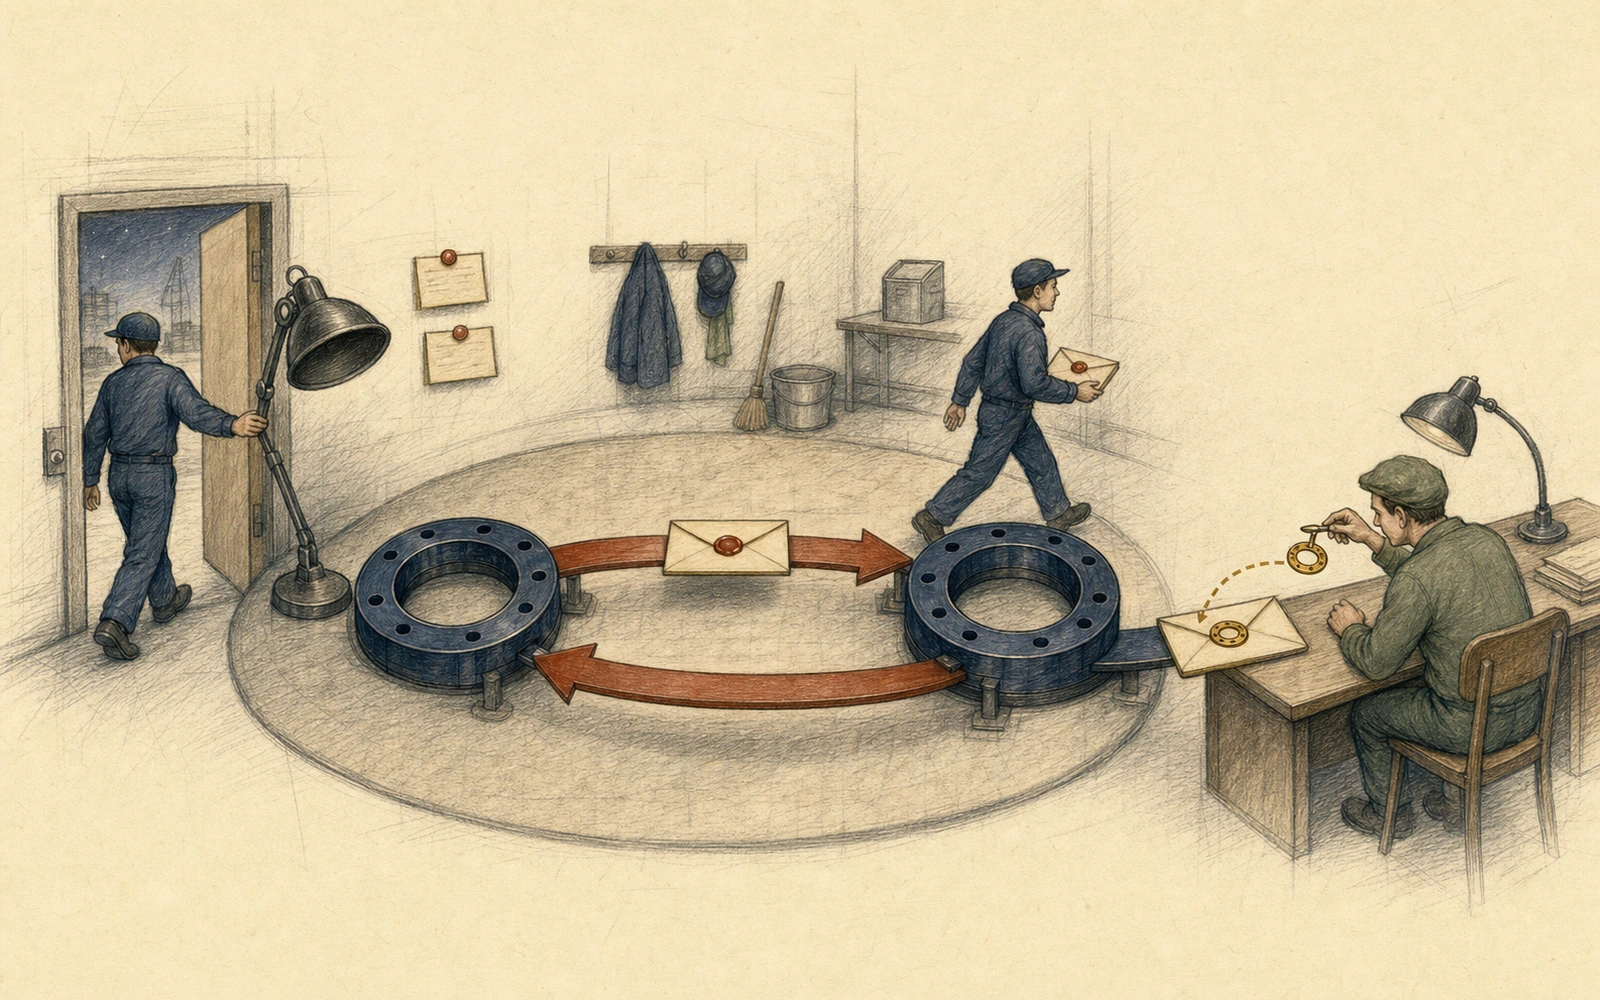
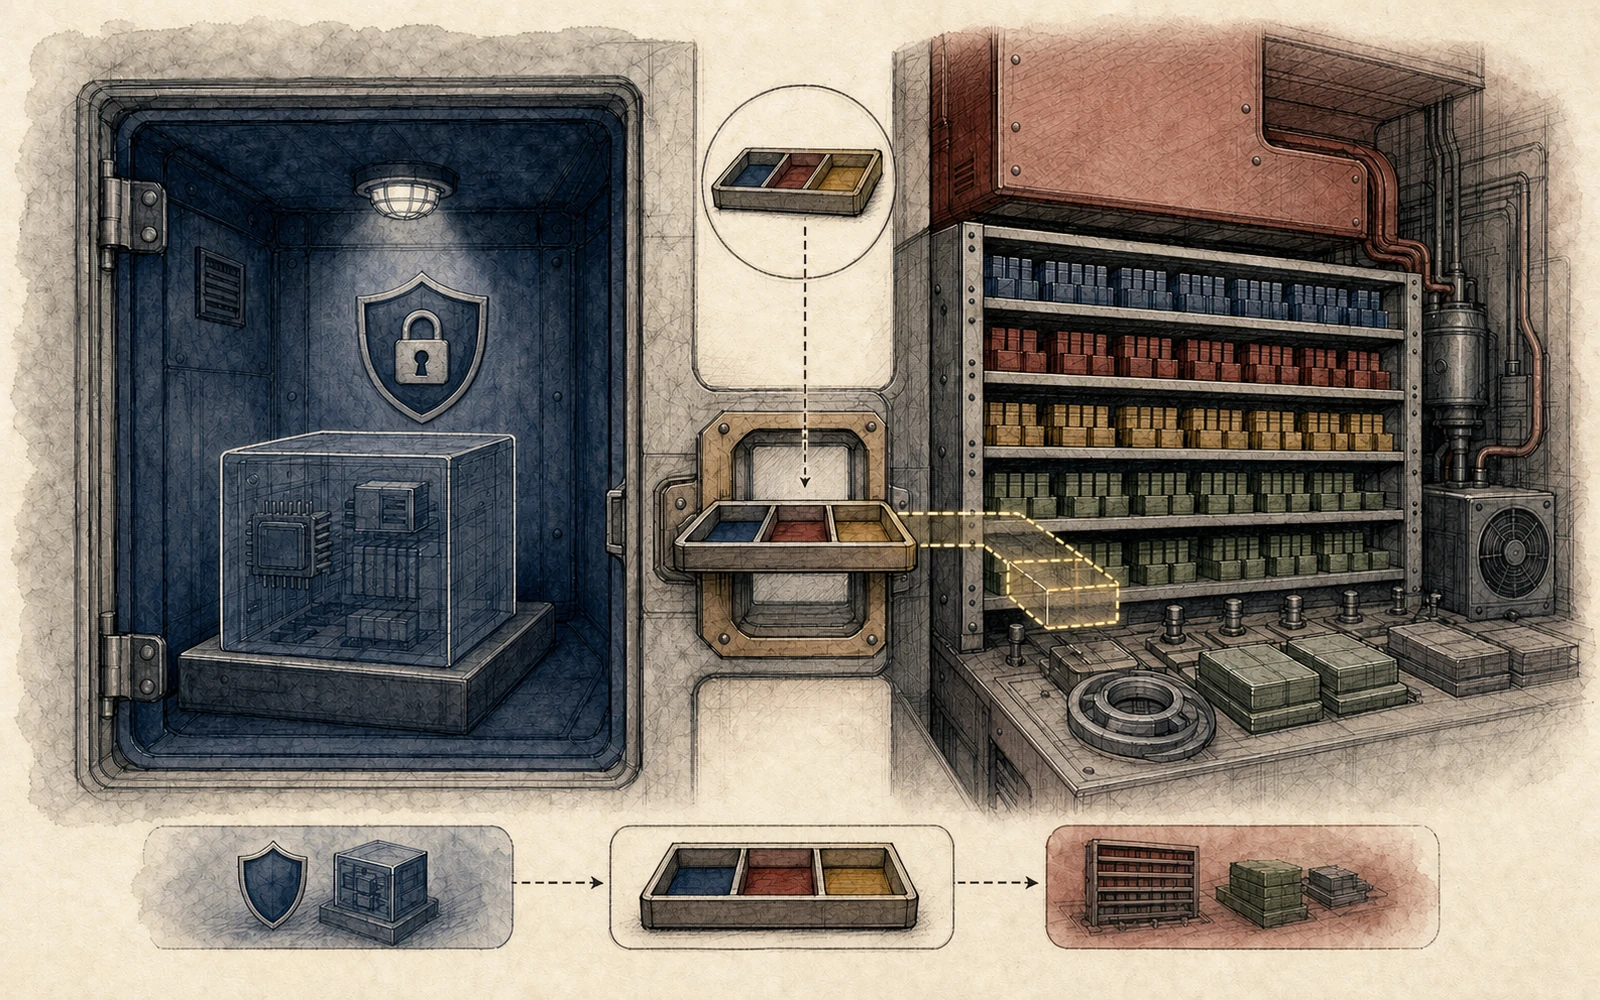
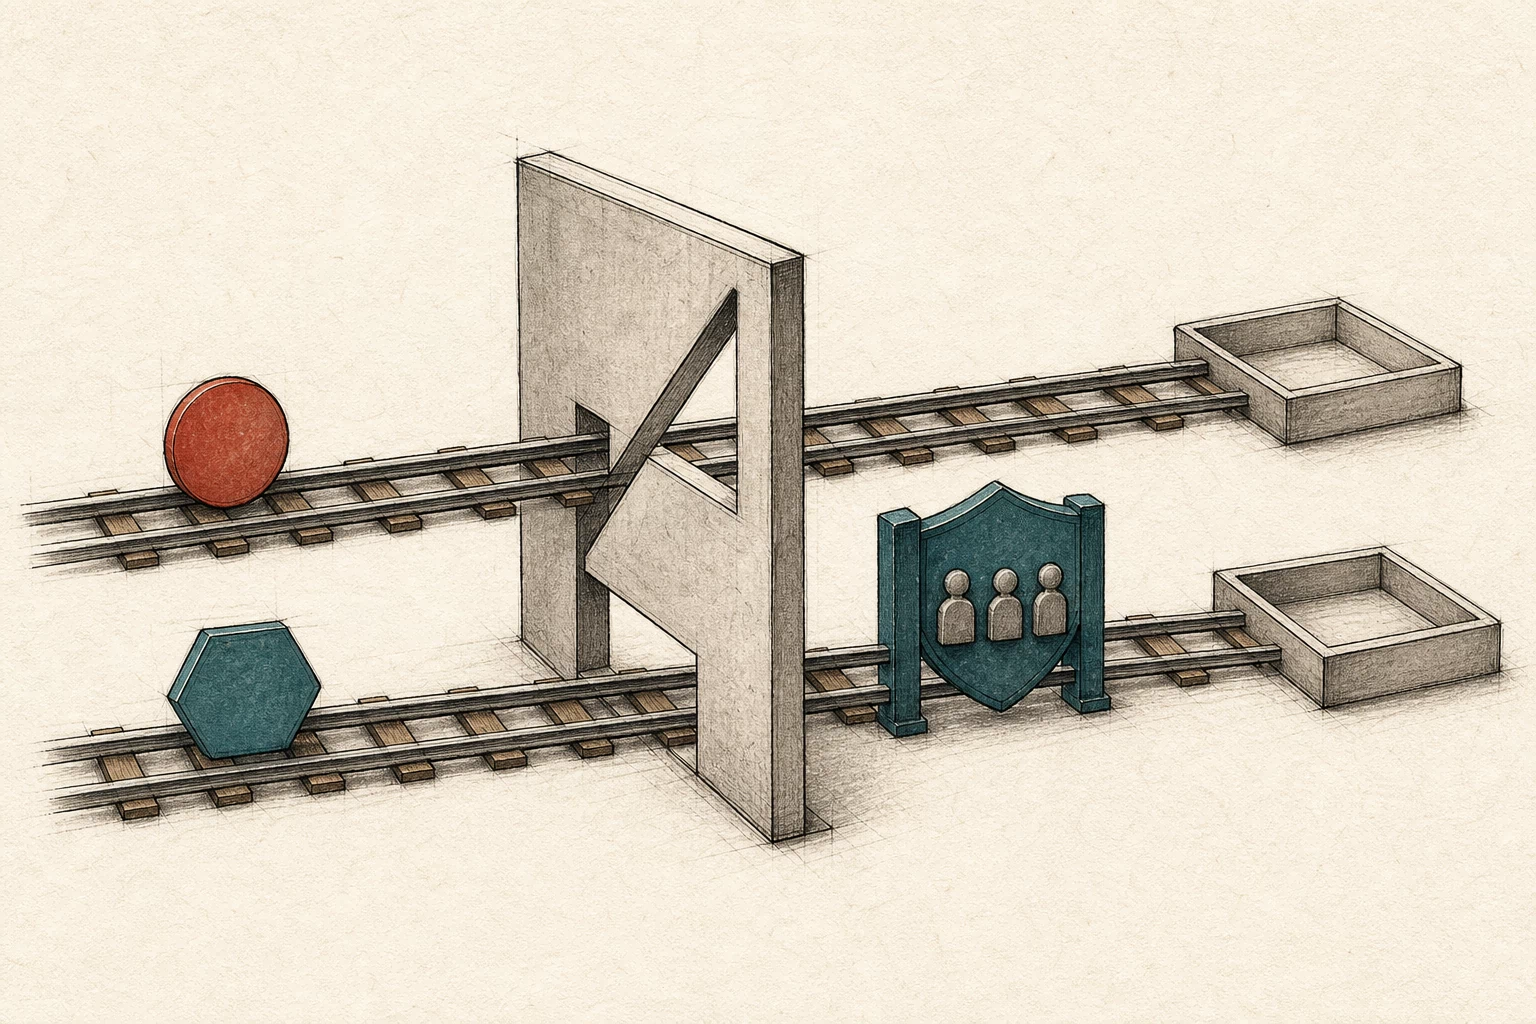
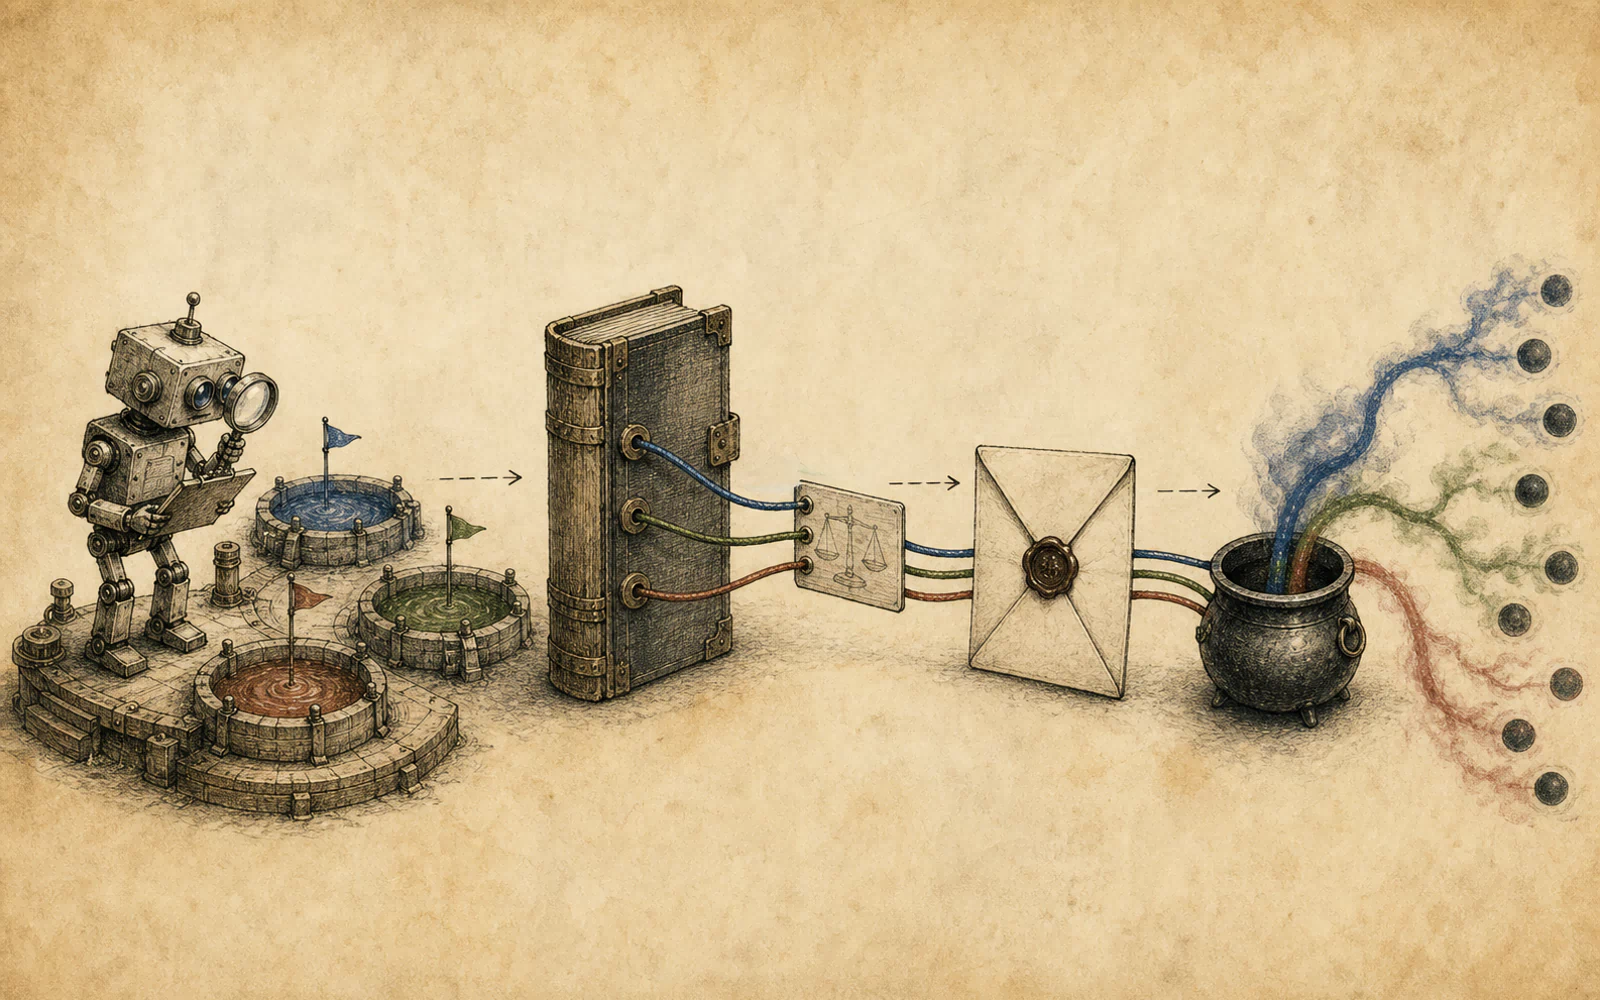
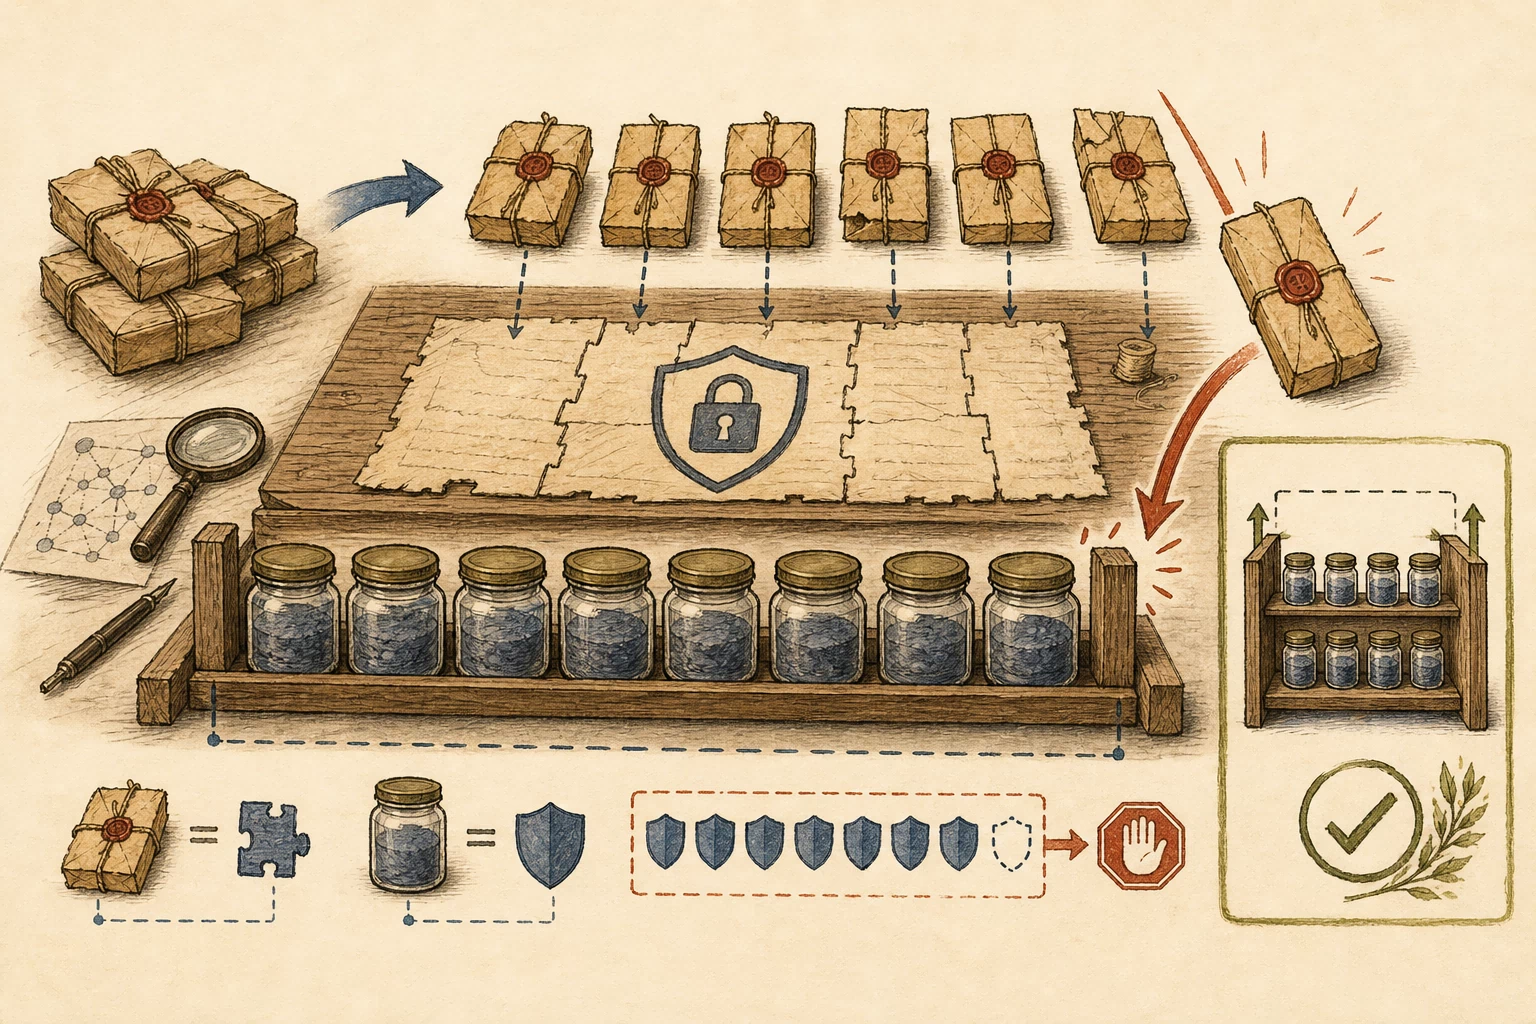
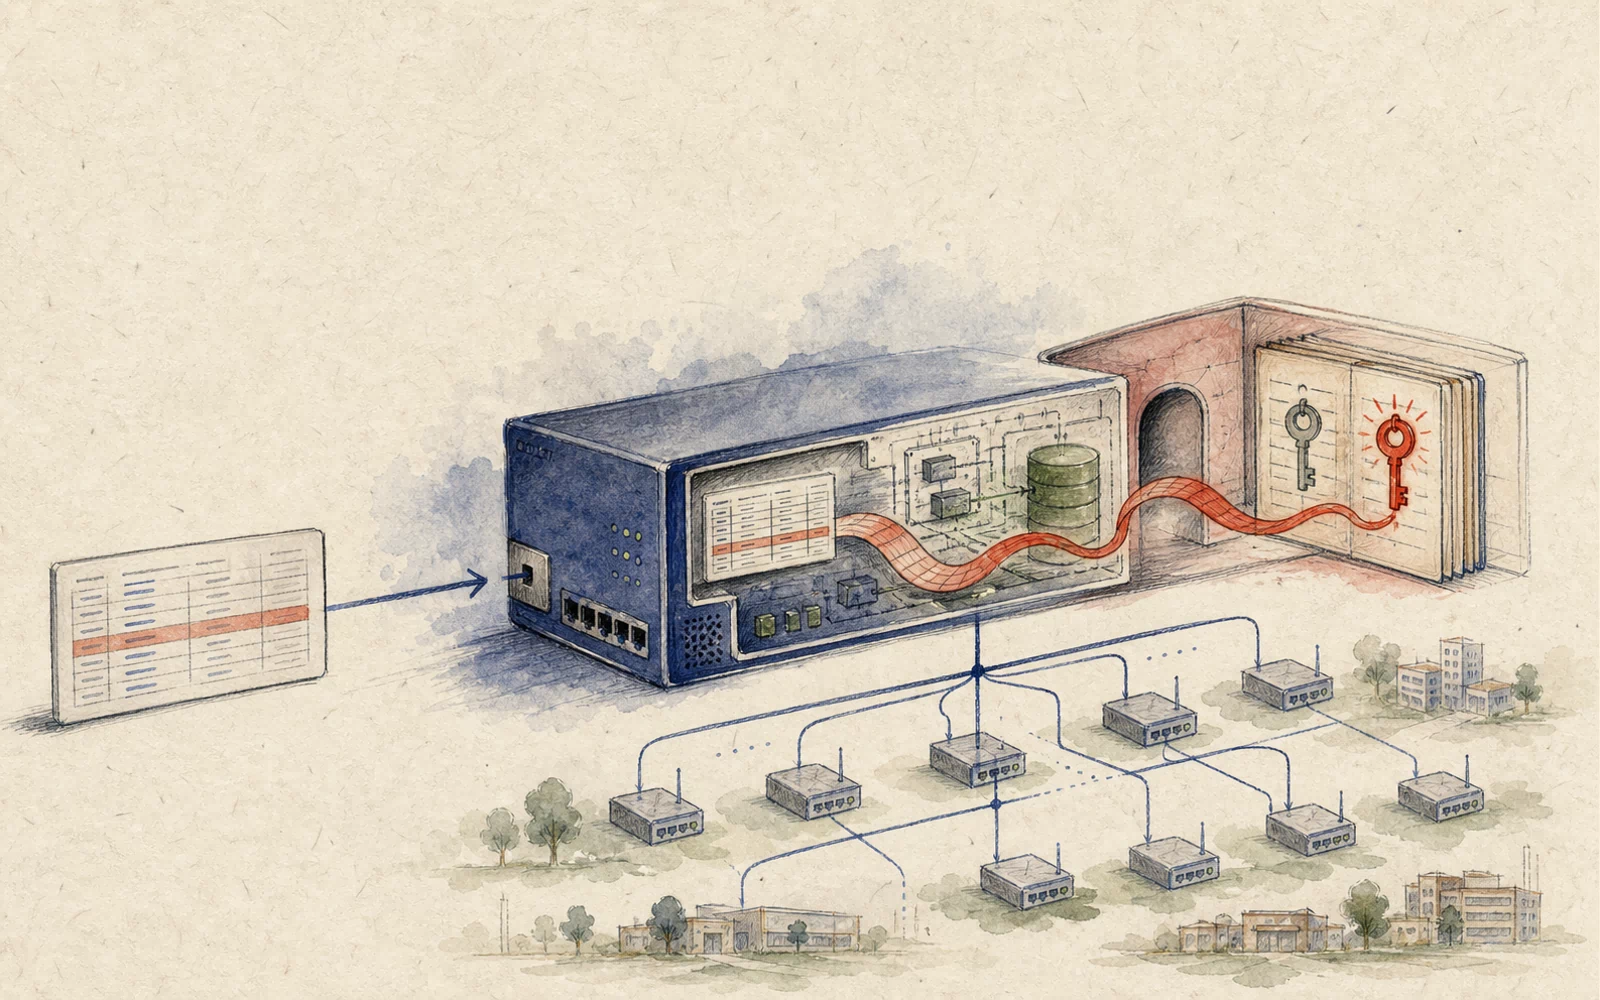
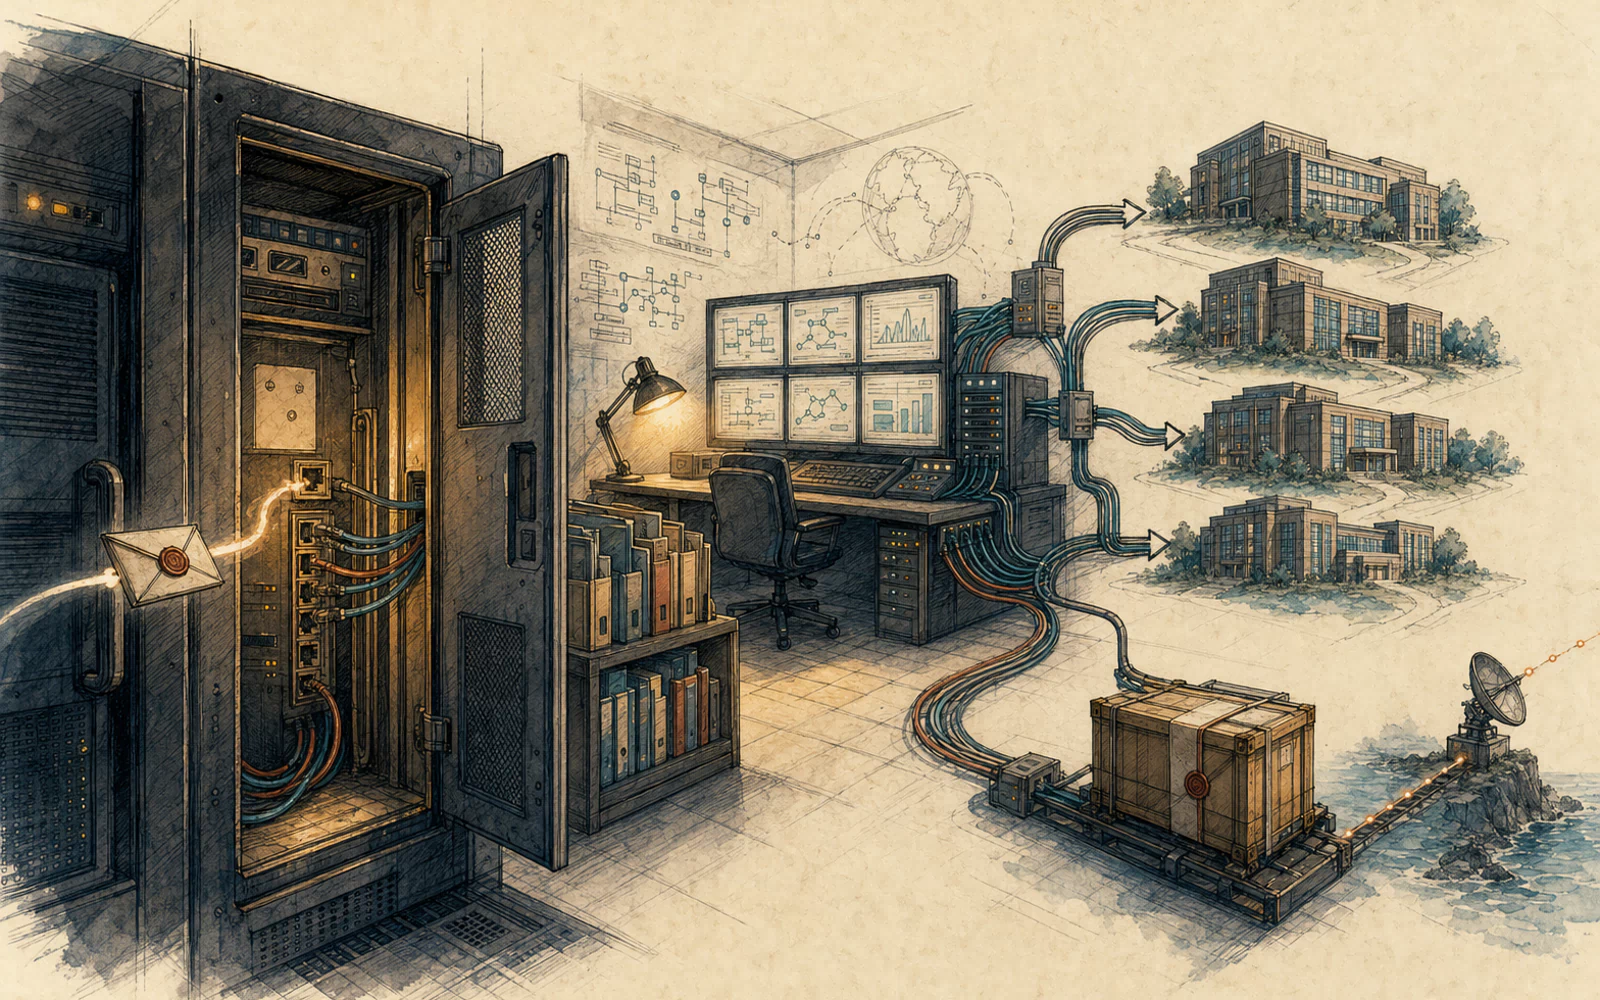
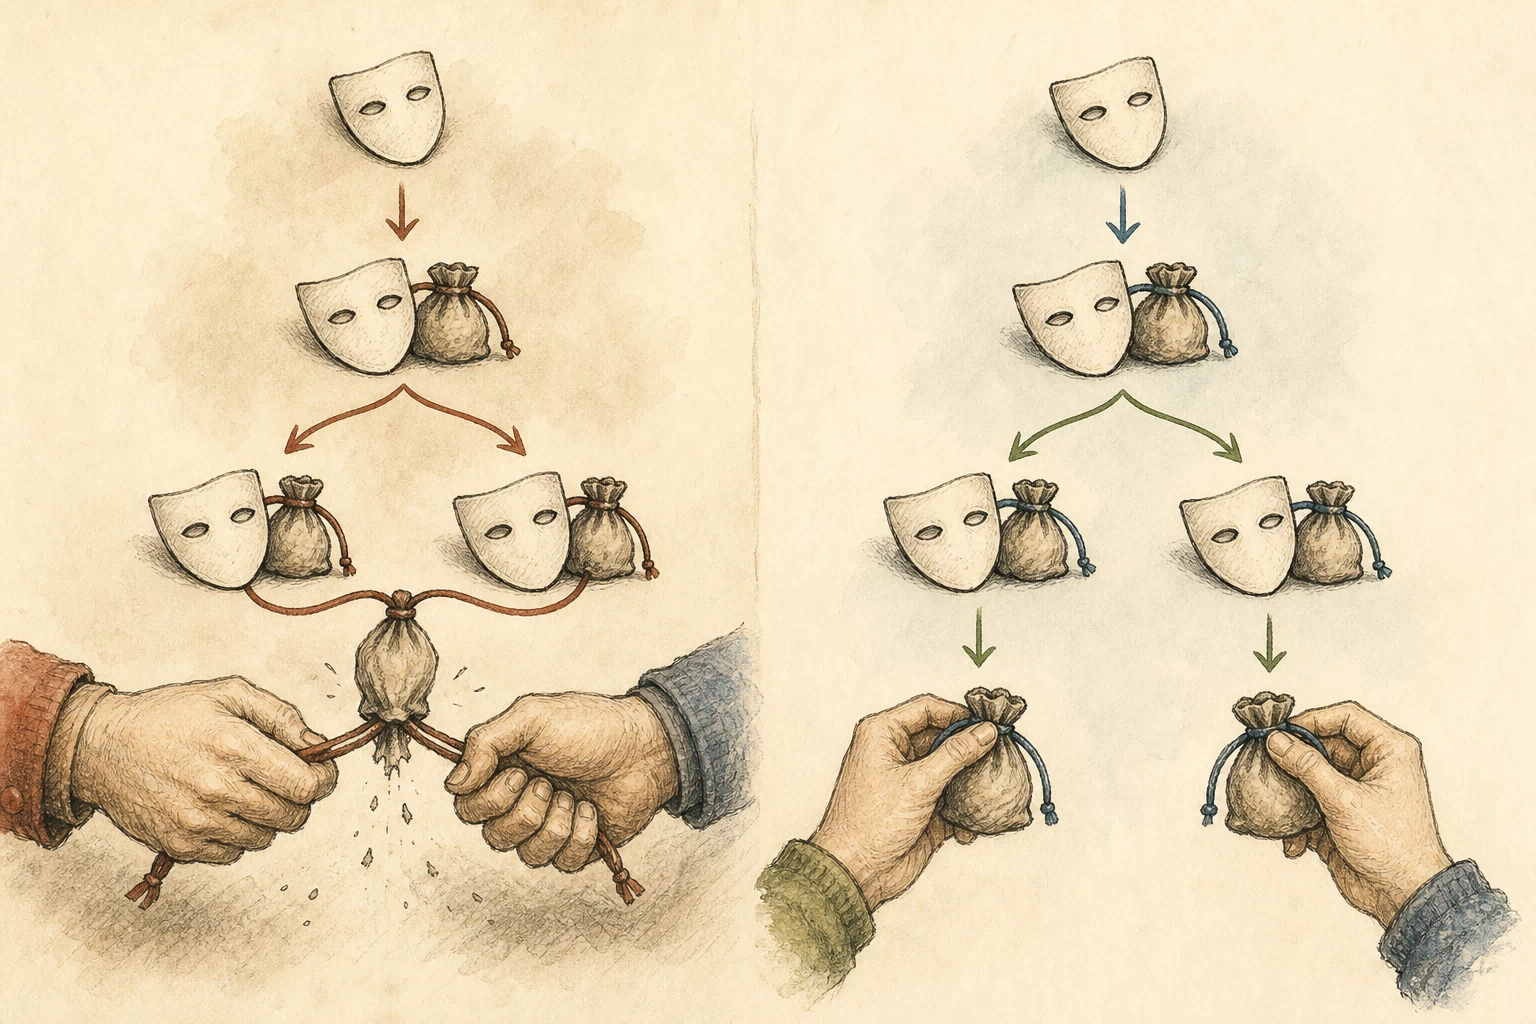
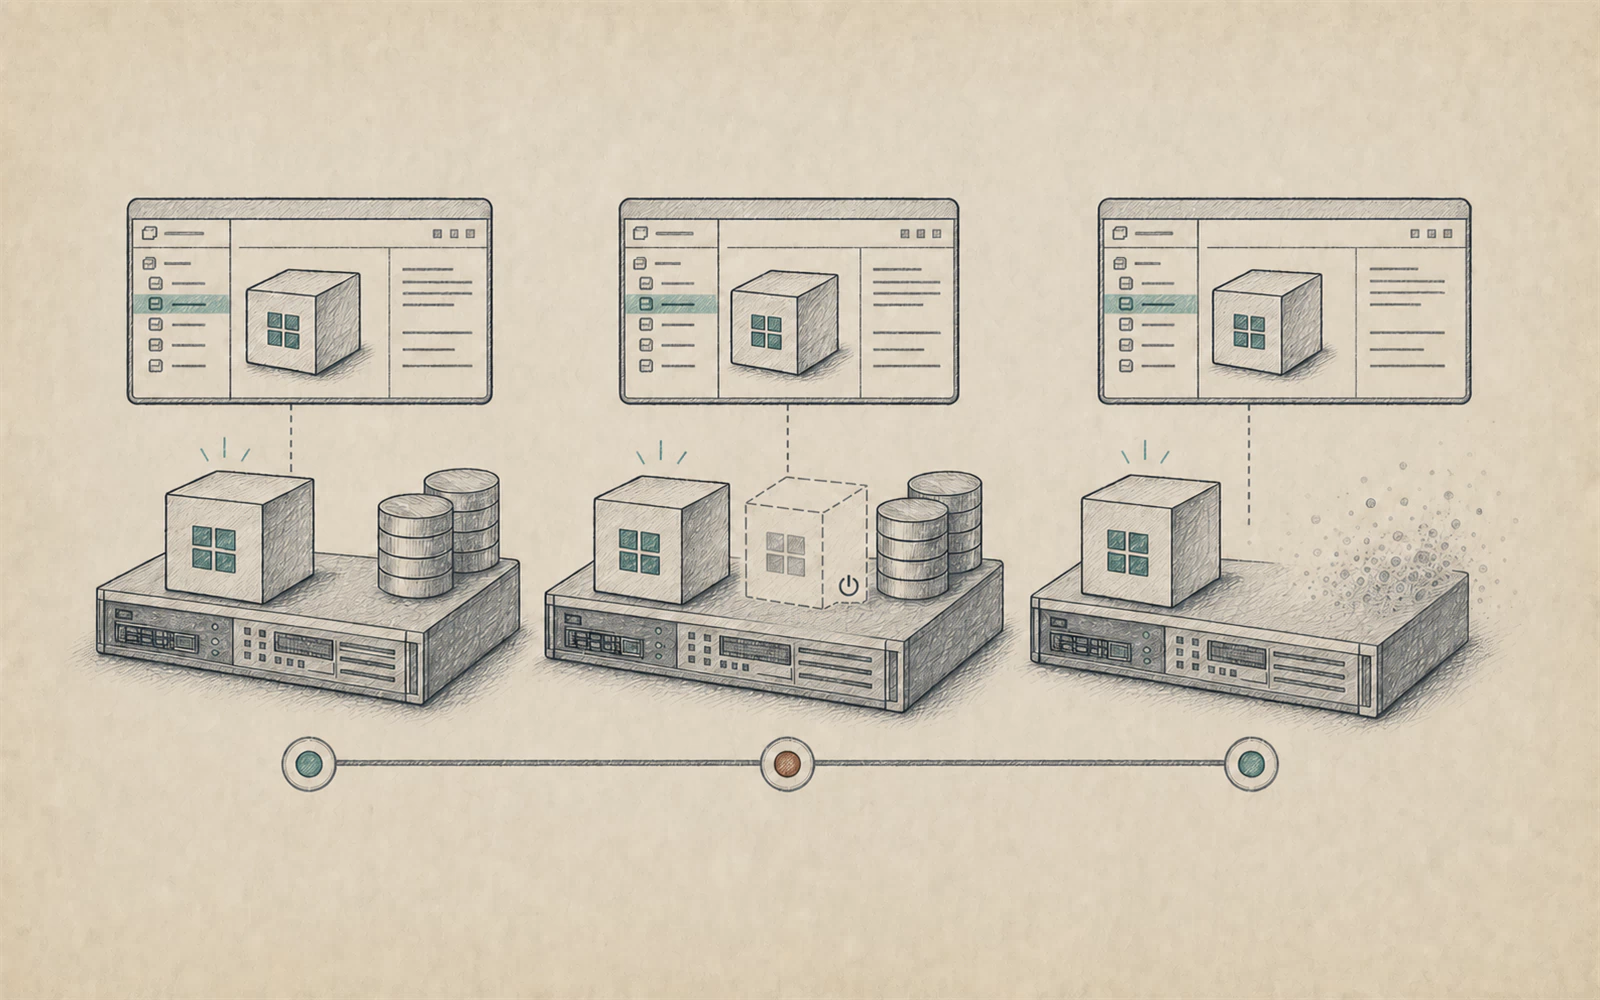
PwnEscape: how a VM's outgoing packets exposed host memoryThe host finishes a VM's checksum but writes the result into an IPv4 header it has already checked. Fragmentation then trusts the altered header length. In the researchers' example, it copies 32 extra bytes, sending host memory out with the packet. Fixing CVE-2026-99999 requires updating the host kernel. Updating only the system inside the VM leaves this code unchanged.
- Identifier
- CVE-2026-99999