Vulnerability research
Cisco SD-WAN: one login, network-wide authority
Cisco has confirmed exploitation of CVE-2026-76504, an authentication bypass that grants SD-WAN Manager API privileges. Patch within the existing release train, then establish whether anyone used that access to change the network before the fix.
In this article
The network can keep forwarding traffic while the person controlling it has changed. On September 30, Cisco disclosed an authentication bypass in SD-WAN Manager and confirmed exploitation during September. An attacker could gain administrative API privileges without first obtaining an administrator's password. In a system that centrally manages branch networks, that position deserves urgent attention: a Manager can reach far more configurations and devices than its own operating system.
CISA added it to KEV on disclosure day. Cisco assigns a CVSS 3.1 score of 9.8, while confirmed exploitation makes the urgency more concrete. The disclosed entry point is small: one character in a request path is written using percent-encoding. Following a normal login shows why the rule protecting that path matters.
1 What a successful login gives the browser
SD-WAN Manager was previously called vManage. Administrators use its web interface to configure the network, while automation can call its APIs. Both ultimately depend on the same decision: which user owns this request, and what may that user do?
Cisco's authentication documentation describes the normal exchange. The client submits a username and password to /j_security_check and receives a JSESSIONID session cookie after authentication. It then uses that cookie at /dataservice/client/token to obtain a CSRF token. Most state-changing POST requests carry the session and an X-XSRF-TOKEN header. The second token helps associate requests with an established session; that session still needs a trustworthy identity.
The PSIRT advisory confirms administrative API privileges as the result of this vulnerability. Once an identity has been accepted incorrectly, subsequent API operations run under that authority. A stronger administrator password cannot repair a path that bypasses authentication. Multi-factor authentication on the ordinary login flow likewise cannot complete a check for a request that failed to enter that flow correctly.
How far can those privileges reach? The documented interface includes retrieving a device's running configuration; Manager also administers network policies and management accounts. An investigation therefore needs to follow management operations into the actual device configuration. Public reporting has not detailed the actions in each victim environment, and compromise of downstream operating systems remains a separate question to investigate.
2 One character, two spellings
Percent-encoding is ordinary URL syntax. %20 represents a space, and %6a represents a lowercase j. RFC 3986 permits normalization of unreserved characters such as letters: their encoded forms can be decoded to the same character for comparison. This rule cannot be extended indiscriminately to reserved characters. Decoding a path separator, for example, can change the structure being interpreted.
Cisco's detection guidance uses /%6a_security_check as an example. A reader can readily connect it with /j_security_check. Software that uses different representations at different stages can apply a protection rule to one spelling while processing the request as another. Cisco identifies improper URI encoding handling as the cause, allowing an authentication rule protecting a particular API endpoint to be bypassed.
The failure gave different spellings of the same endpoint different protection. Cisco has not published the relevant functions or full patch, leaving the components that retain and decode the path unidentified. The gate in the diagram represents the authentication rule; the advisory does not locate its implementation in a particular layer.
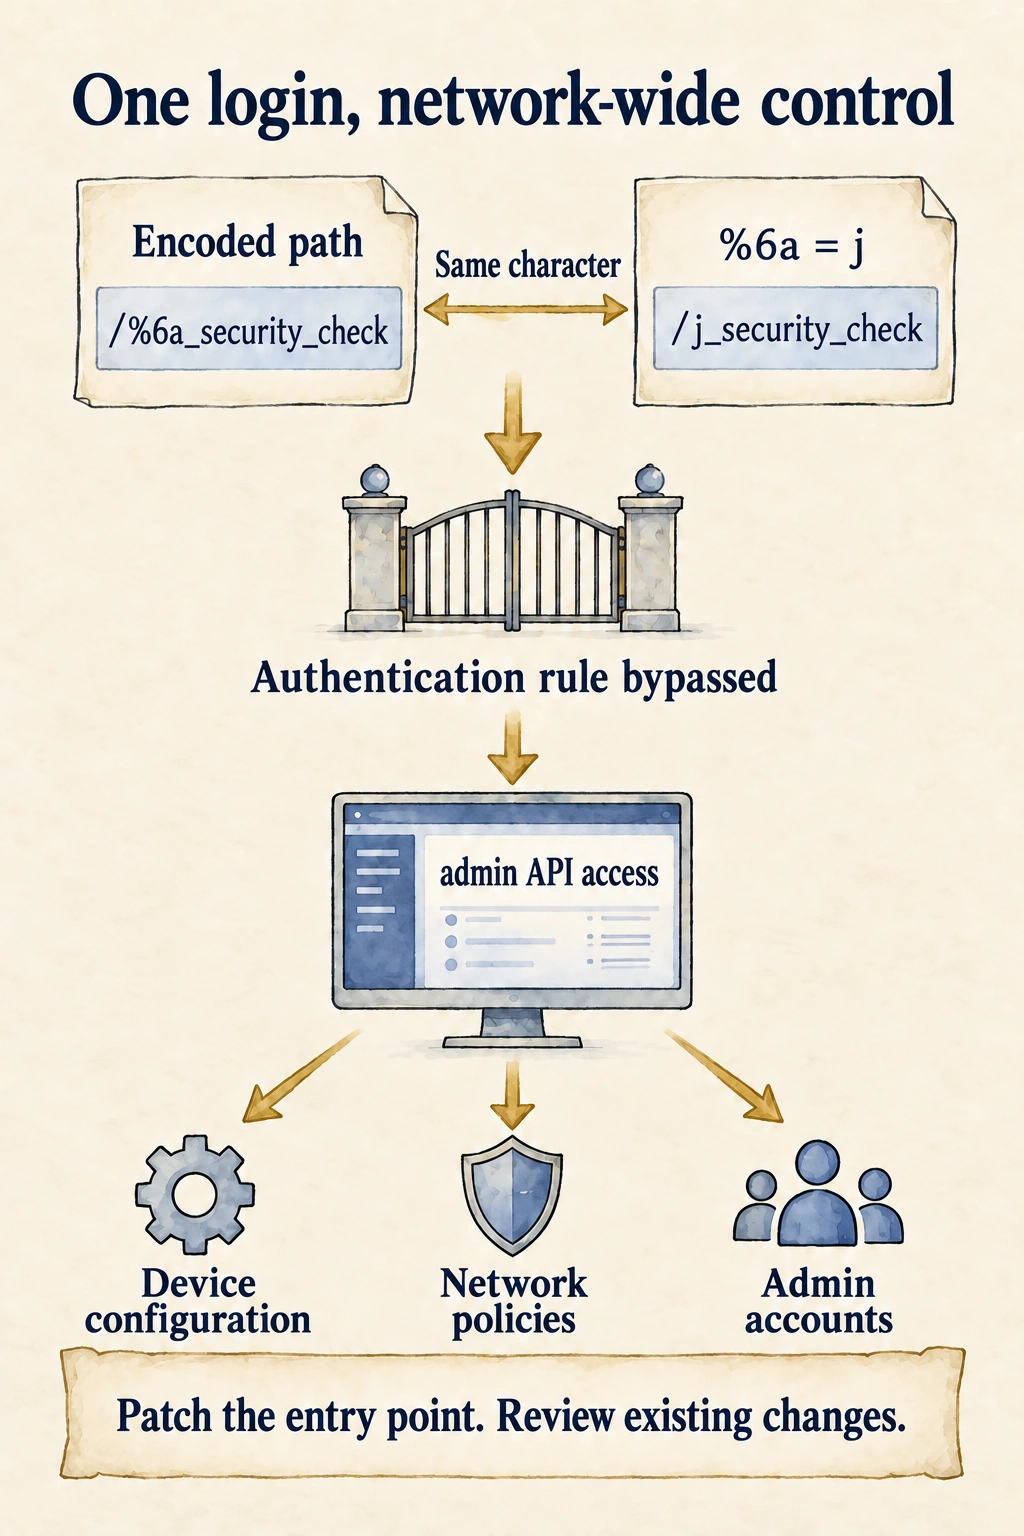
%6a and j represent the same character. The lower objects show what the management APIs can reach.This explains why blocking one string is fragile. Cisco explicitly warns that other characters in the path can also be encoded. Matching only %6a misses equivalent representations and leaves the server-side authentication defect in place. The product needs to align the endpoint a request addresses with the authorization rules that govern it before deciding whether to execute it.
When reviewing a similar system, compare the path used for authorization with the one used for routing, then establish the order of case handling, percent-decoding and path normalization. Regression tests should confirm that ordinary and equivalent encoded forms receive the same authentication decision while valid API calls still complete.
3 Preserve the logs, then patch within the train
Cisco's October 1 remediation guide calls for an admin-tech bundle from every Manager, including Log and Tech without Core. Save those bundles, then arrange the fix without waiting for TAC's IOC scan. Remain on the existing release train unless TAC explicitly advises a move.
As of October 2, Cisco specifies the following train-specific upgrade targets. Each is also the first release in that train to fix this vulnerability.
| Existing Manager train | Repair target |
|---|---|
| 20.9 | 20.9.10.1 |
| 20.12 | 20.12.8.2 |
| 20.15 | 20.15.6.1 |
| 20.18 | 20.18.4.1 |
| 26.1 | 26.1.2.1 |
| 26.2 | 26.2.1 |
Releases before 20.9 require migration to a supported train. Include every Manager in the cluster, primary site and disaster-recovery site; checking only the node currently serving the GUI leaves gaps. This vulnerability concerns Manager. Cisco's treatment of Controllers and Validators assumes that those components already received the August 2026 security upgrades. For example, it permits fixed Manager 20.15.6.1 with Controller and Validator 20.15.6. Environments that missed the earlier upgrades need to complete the vendor's component sequence. The Manager table is not a compatibility matrix for the entire fabric.
Cisco Managed Cloud 20.15.605 already contains the fix and requires no additional customer action; the Help screen can confirm that release. Other cloud-hosted overlays have their own upgrade arrangements. Their operators should check change windows and installed versions in the self-service portal.
While an upgrade is pending, restrict network access to the management interface to genuinely necessary trusted sources. This reduces reachability and can interrupt administrators or automation connecting from other addresses. Cloud portal Allow Inbound rules should likewise retain only necessary management prefixes. Cisco offers no workaround that fully substitutes for the fix. If an upgrade fails, retain those restrictions and work with TAC on a compatible, fixed recovery path. Returning to a vulnerable release reopens the entry point; a working login page is insufficient evidence that recovery is complete.
4 Follow the request into the changes it made
Pre-upgrade material answers a question the patch cannot: was this entry point used before the repair, and what happened afterward? Cisco recommends submitting admin-tech bundles to TAC for IOC scanning. When generating a bundle is impossible, collect serviceproxy-access.log, vmanage-server.log and rotated logs according to the vendor's instructions. The advisory and subsequent guide spell the service-proxy directory differently, so locate the files in the actual installation instead of treating either absolute path as universal.
Clues include encoded j_security_check requests and activity involving viptela-reserved-* accounts. These help narrow the time window. Correlate a hit with its source address, response, session, account and later operations. Cisco cautions that authorized scanning and normal activity may produce similar records. Omitting rotated files or another cluster node can remove the earlier part of the sequence.
Read the response as well as its status code. The normal authentication documentation notes that an unauthenticated request may receive an HTML login page; HTTP 200 alone therefore cannot establish successful exploitation. Conversely, unplanned account, policy or configuration operations nearby in time warrant following the affected objects. Trusted configuration backups, approved change records and current device state help distinguish a request reaching an entry point from a management change taking effect.
A device can retain its configuration after Manager has been upgraded. The patch restricts future requests; validly formatted configuration previously issued through an administrative API must be checked against change records. Confirmed or strongly suspected unauthorized activity calls for further identity and configuration investigation, with recovery where necessary. TAC's IOC scan does not perform the entire forensic investigation. Environments without detected IOCs still require the upgrade, without delaying it while awaiting the scan.
Recovery exercises for centralized management systems should include downstream devices. Policies and accounts may remain active after the management application is restored. Keeping comparable configurations and change records during normal operation makes it possible to find and reverse unauthorized changes during an incident.